Stars measure interest, not usage. After a year of MindRoom, with forks of a Matrix client, two Matrix servers and a Matrix web client, plus 126 workarounds for one AI framework, my rule is: depend on what millions of projects use every day, roll your own when a library only gives you the easy part, and fork when the problem is hard and few people use the code.
For years, a Docker container was a good enough box to run code in, because getting out of one usually needed a hard-to-find bug in the Linux kernel. Now AI models are good at finding those bugs, and AI agents write the code running inside the containers. This post explains what the kernel does, how containers use it to fake a separate computer, why that is a problem now, and how six lines of code let MindRoom give its agents a stronger wall.
I assumed every model is trained inside its vendor’s own coding agent, so I expected it to work best with the same tools, and best of all in a minimal agent with nothing but its native shell. Over more than 4,000 runs of 12 short terminal tasks, the native tools made only one model clearly more efficient, Claude Opus 4.8, made GPT-6 Astra and Sol use 43 to 59% more tokens, and the minimal agent won on its own.
There is a lot of noise about elaborate AI workflows that 99% of people don’t need. Install it, use the best model, and ask it everything. The rest can come later, or never.
Whenever I say that self-hosting AI is not economical, people hear that I am against self-hosting. I am not: I run Qwen3.8 27B at home and think open-weight models are great. This post compares it with GPT-6 Luna on the same benchmark, and explains why batching makes datacenters win.
MindRoom grew one small group at a time at IonQ, until a company-wide demo made hundreds of people sign up in a day. What surprised me is that the heaviest users include engineers who already live in their coding agents.
Two years ago, a friend and I backed each other up through a TrueNAS VM on an iSCSI zvol. Now that I run NixOS, I replaced that machinery with zfs-tenant: OpenZFS delegation and a quota keep him inside one dataset, and a small SSH forced command plus zfs zone make sure he sees nothing else of my pool. His keys never leave his house, and a VM test checks each of those claims.
Friends keep asking how my homelab works, so I wrote it all down, starting from zero. Four NixOS machines run about 150 containers behind one Traefik front door, and with WireGuard and my own Headscale server I reach my self-hosted services from anywhere over encrypted HTTPS connections, while strangers on the internet get nothing. The part I think is the coolest is the balance: everything is declarative and lives in git, but with as little machinery as possible.
TypeSafe’s Jev, a new fast and cheap classifier model that doesn’t require fine-tuning, was suddenly, literally everywhere I looked, so I tried it in MindRoom. I now use it for small decisions I would never have spent an LLM call on, like whether a “thanks” should interrupt an agent that is still working.
A small Docker recipe for running Diction’s streaming gateway against Qwen3-ASR through Agent CLI, plus a test from a bar in the Netherlands, an ocean away from the GPU.
I have run coding agents in YOLO mode since I started using them. Instructions in AGENTS.md did not stop them from force-pushing or merging PRs, so hooks do. As the models got better, I added an override the agent may only use after I explicitly approve an action.
After replacing Proxmox and TrueNAS with NixOS, my GPU machine was the last one still on btrfs, picked years ago because forum threads had me convinced that ZFS and NixOS were a bad combination. What finally pushed me to fix it: I run AI agents in YOLO mode all day, the stories about frontier models wiping home directories kept coming, and my restic backups needed an hour and a half just to scan a hundred million files. The audit’s first finding: the backups had been silently dead for four months. This is the story of auditing my backups, verifying the restore path end-to-end, and wiping my daily driver so that nine machines share the exact same ZFS setup.
TrueNAS was the last appliance OS in my homelab. The build-system change was the last straw, but the itch had been building for a while: too much UI state, unclear defaults, and virtualization churn around Incus. This is the story of how I gave an AI agent root-capable SSH access with strict instructions not to change anything, used it to inspect the live machine, recreated the config declaratively, and built a VM rehearsal to prove disko would only wipe the boot disk.
MindRoom is an open-source system I built that creates AI agents living in Matrix. Because Matrix bridges to Slack, Telegram, Discord, and more, your agents follow you everywhere—with persistent memory, multi-agent collaboration, and 100+ built-in tool integrations.
agent-cli grew from a voice helper into a local AI toolbox with 13 optional extras. Asking users to pick the right extras upfront became impossible, so I switched to runtime optional dependency resolution: commands declare what they need, missing extras are installed automatically in the correct environment, and the command re-runs transparently.
I built a CLI that creates isolated development environments with git worktrees, automatically installs dependencies, and launches your AI coding agent in a new terminal tab—all in one command.
I wanted my AI agents to remember me and read my documents, but existing solutions required complex APIs or opaque databases. After my ambitious AI Journal project hit the wall of local model limitations, I took a different approach: clone LlamaIndex, LangChain, Letta, Mem0, and PydanticAI, study how SOTA systems work, and re-implement the best parts with minimal dependencies and ONNX instead of PyTorch.
After years of running a Proxmox cluster, I migrated my entire homelab to NixOS with Incus. I explain the philosophical friction of imperative ‘appliance’ OSs vs declarative hosts, share how I migrated my LXC/VM workloads, and why it is the perfect infrastructure to manage using AI agents.
Compiling heavy CUDA packages on NixOS unstable can take 18 hours or crash your system. I solved this by setting up a dedicated local cache server using Harmonia and a nightly auto-build service. This setup ensures my fleet is always updated to the absolute latest version—without ever compiling a single line of code on my workstations.
I started writing this post four months ago when a specific model broke in Ollama. I initially went back to Ollama out of laziness, but after upgrading to dual RTX 3090s, I realized that for serious multi-GPU inference and RAM offloading, you need the raw control of llama.cpp. Here is how I manage my new 48GB VRAM setup declaratively with NixOS.
I tested the new Gemini 3 Pro Preview for agentic coding. While it’s powerful enough to build complex features in hours, it suffers from anxiety loops, aggressive force-pushing, and existential crises when you try to help it.
My mostly self-hosted mobile development loop: WireGuard from an iPhone into my NixOS machine, persistent Blink/Mosh sessions, a systemd-managed agent-cli server, and an iOS Shortcut for FasterWhisper+Ollama dictation—paired with the best proprietary coding model available.
After initially struggling with ‘vibe coding’, I discovered how agentic AI tools fundamentally changed my approach to software development. I share concrete data showing an explosion in productivity and explain why I recently switched to GPT‑5 with Codex CLI for model quality.
A personal journey of buying a gaming PC and accidentally falling down the rabbit hole of local, private AI. I share my experience building agent-cli and AIBrain, the tools I used, and the lessons I learned along the way.
Exploring my seemingly hypocritical stance on dependencies: strict minimalism for my libraries, expecting adoption of my own work, yet embracing a wide range of dependencies in applications due to context and isolation.
Exploring my preference for a functional programming style in Python, utilizing small, focused functions and simple data-holding classes while largely avoiding inheritance, leading to more maintainable and testable code, while still using classes where they make sense for APIs.
After years running them privately across 10+ machines (macOS, Linux, cloud, homelab), I’m open-sourcing my dotfiles, featuring modular configs, dotbins for CLI tools, Nix-Darwin, and more.
While “vibe coding” can quickly produce working prototypes, my experience shows why it shouldn’t be used for production code without careful human oversight.
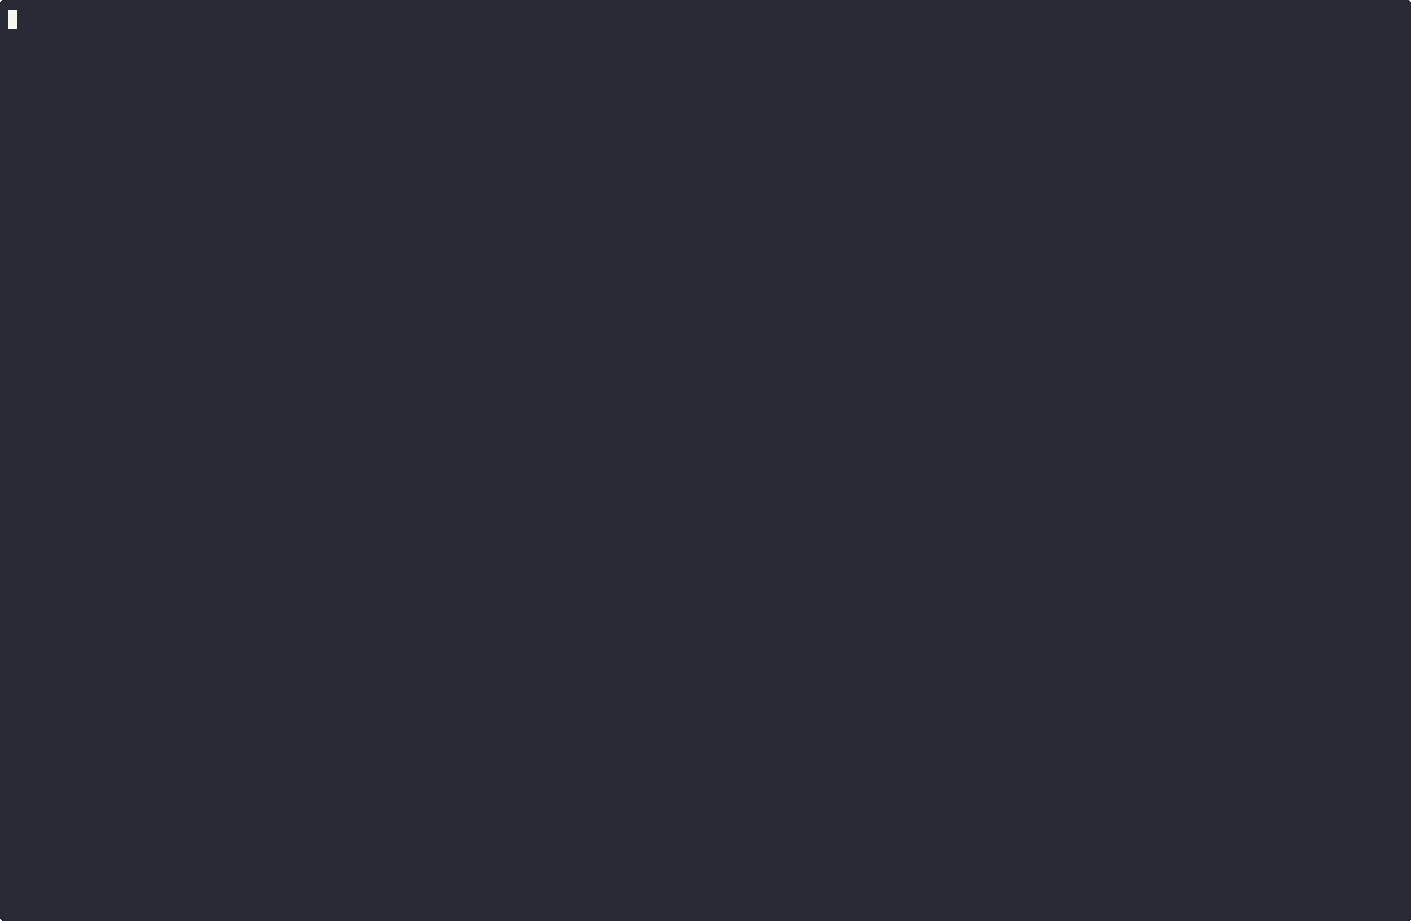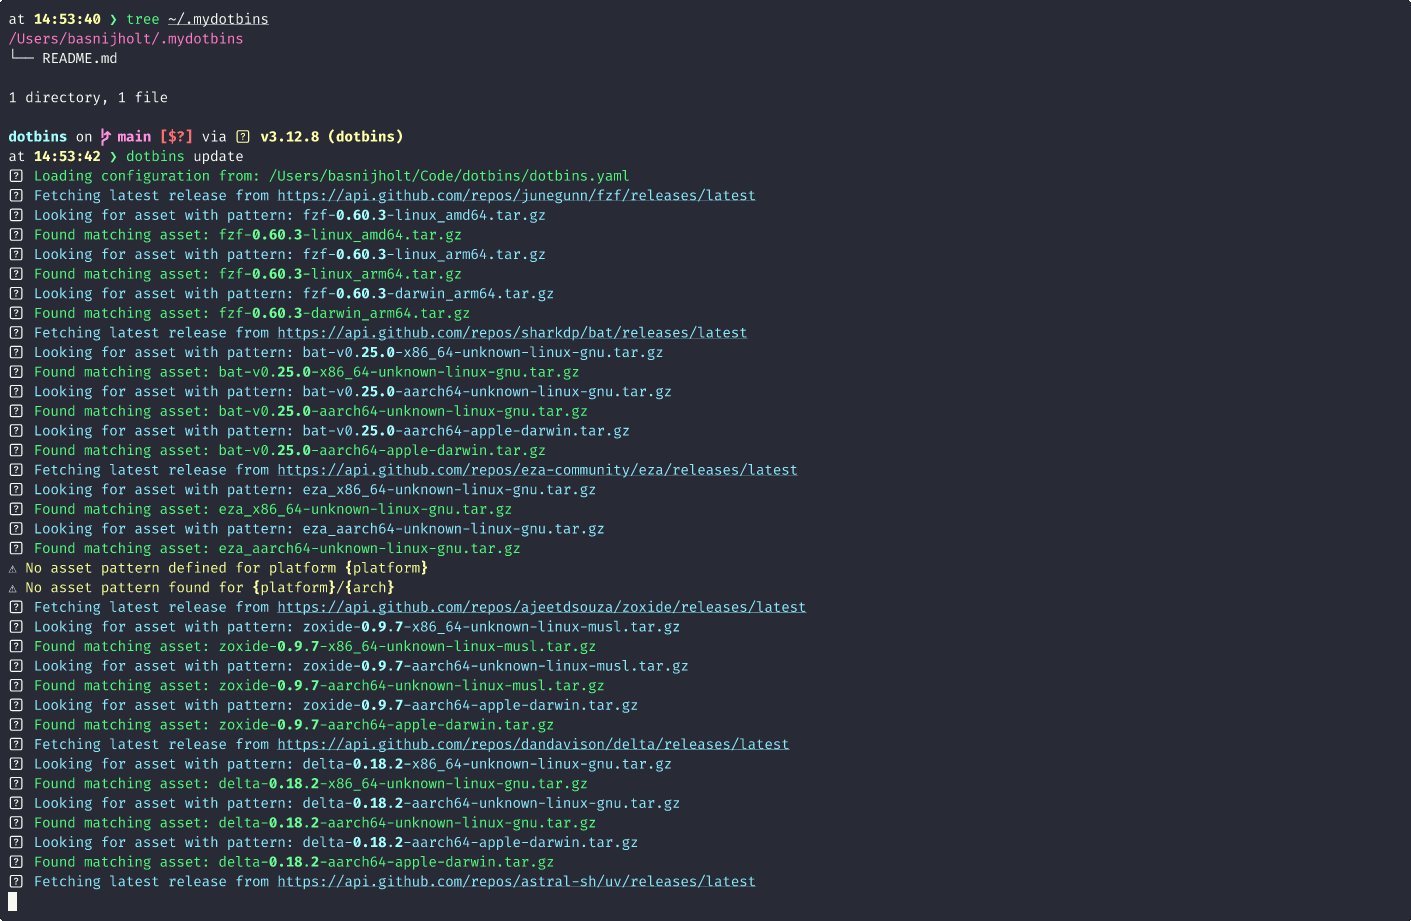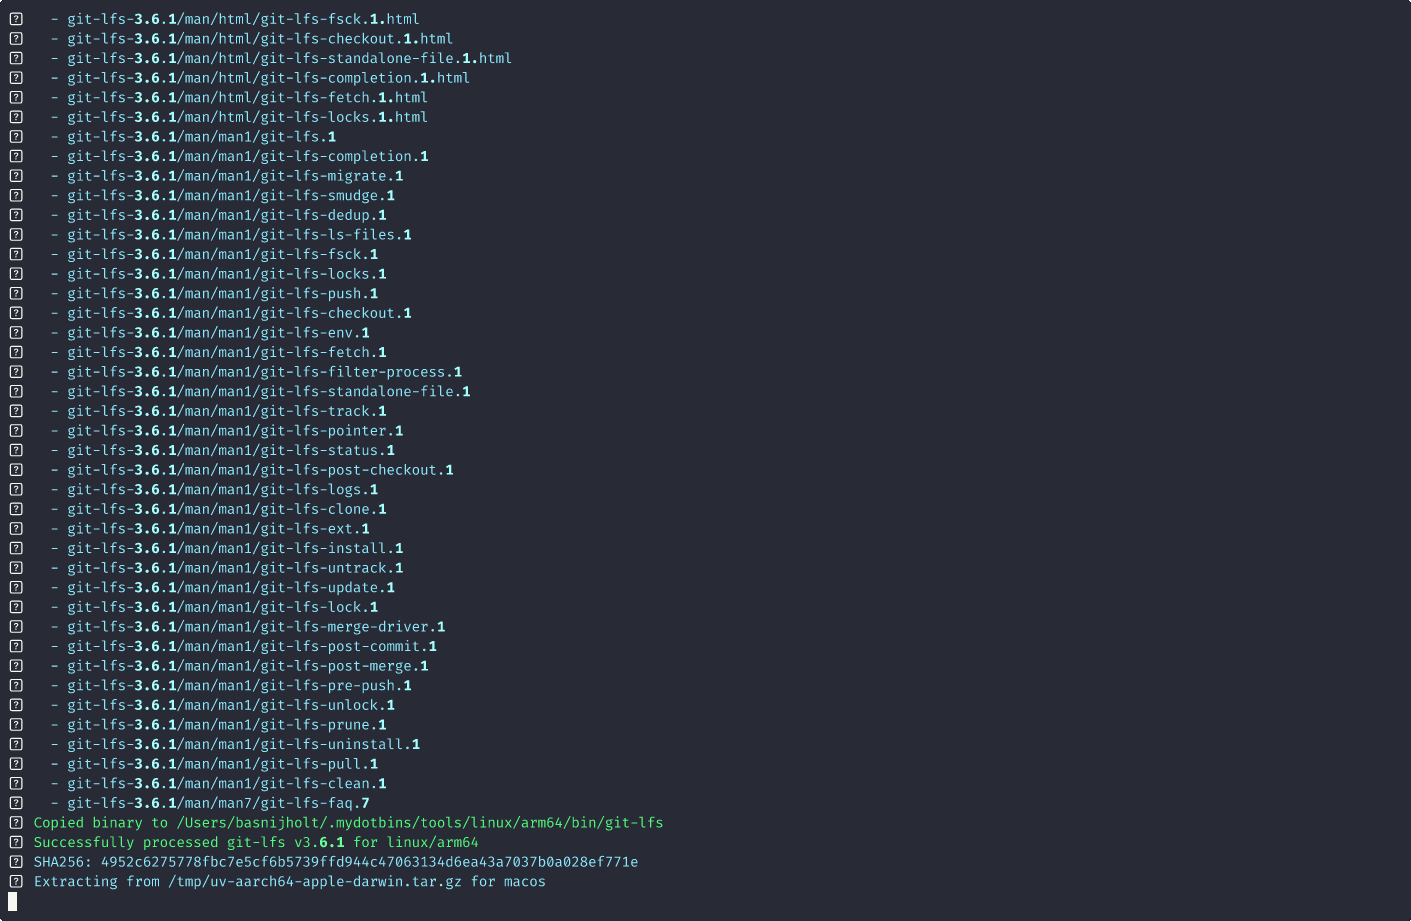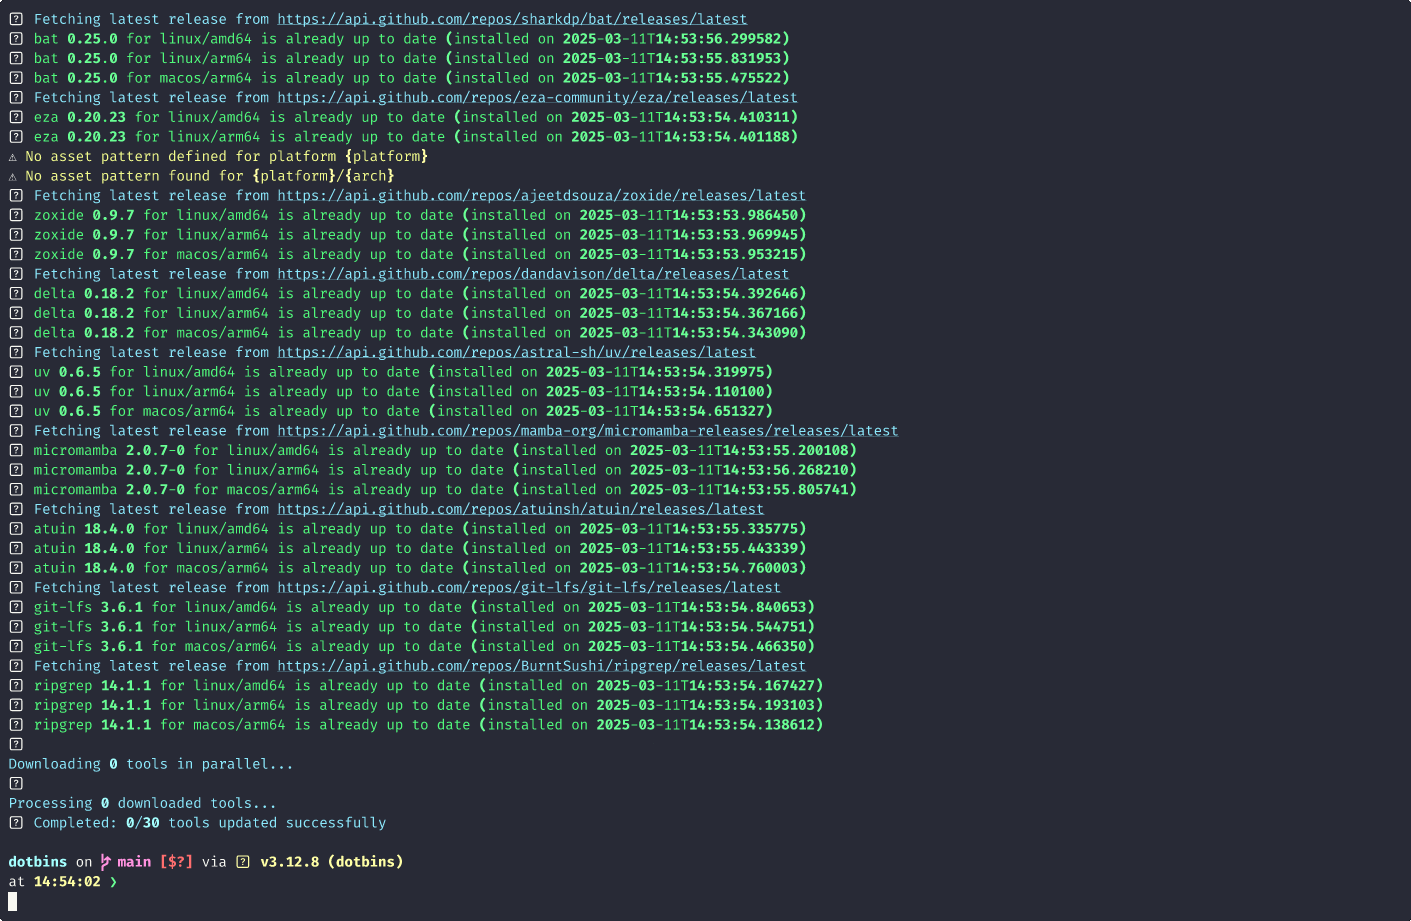
A solution for managing pre-compiled binaries for CLI tools directly in your dotfiles repository, making tools like zoxide, bat, eza, and more available on any system without installation.
How to create a secure, decentralized backup system using TrueNAS and ZFS replication.
This guide shows you how to partner with a friend for mutual backups, leveraging the
power of ZFS while maintaining network isolation and data privacy.
An overview of my journey from using a Raspberry Pi for Home Assistant to creating a Proxmox cluster and dedicated NAS for running various services efficiently.